Step-up authentication should fire for two reasons: the action is sensitive (moving money, changing contact details, exporting data) or the context has become riskier (a new device, an unexpected location, abnormal velocity). The best programs combine both, challenge only at the moment of risk, and answer a failed challenge by holding the action rather than retrying it quietly. This guide lays out the triggers, the thresholds, the challenge methods and the failure handling, anchored in US regulatory and standards guidance.
TL;DR
- Trigger on sensitive actions first (payments to new recipients, credential and address changes, privileged access), then add contextual signals such as new devices and unusual locations.
- Risk signals can justify a stronger challenge, but per NIST they never replace an authentication factor or change the assurance level on their own.
- Prefer phishing-resistant challenges (FIDO2/WebAuthn passkeys, security keys, PKI). Treat SMS, voice and email codes as weaker fallbacks.
- On a failed challenge, deny or hold the action, rate-limit and log attempts, and do not reveal which factor failed.
- Review triggers periodically: spoofing, SIM swapping, push fatigue and deepfake-assisted impersonation keep changing which signals matter.
Table of Contents
- What step-up authentication actually does
- Trigger category 1: the action is high risk
- Trigger category 2: the context has changed
- Combining signals into thresholds
- Choosing the challenge once a trigger fires
- Support channels need triggers too
- Handling a failed challenge
- Keeping triggers current against spoofing and deepfakes
- Perspective
- Where to go next
- FAQ
- Sources
What step-up authentication actually does
Step-up authentication raises an already authenticated session to a higher level of assurance when the requested action demands it. NIST SP 800-63B-4 frames it exactly that way. A customer logs in with a baseline method, browses balances without friction, and meets an additional challenge only when they try something that carries real loss potential.
That is the difference from blanket multi-factor authentication, which asks for several factors at every login regardless of what happens next. Step-up is a policy layer on top of the session: the login establishes who is probably present, and the trigger decides when probably is not enough. Done well, it protects the actions fraudsters want while sparing the majority of sessions that are routine. Done badly, it either challenges everything, which trains customers to click through prompts, or challenges nothing that matters.
The design question is therefore never “should we step up?” but “which events earn a challenge, and how strong should it be?” The rest of this article answers that in order.
Trigger category 1: the action is high risk
Action-based triggers are the most defensible because they do not depend on a model guessing intent. The Federal Reserve’s interagency guidance on authentication and access tells institutions to weigh transaction amount and volume, information sensitivity, irrevocability, and the likelihood and impact of fraud when identifying high-risk transactions. It also lists privileged access and access to critical systems and data as high-risk considerations for users.
Translated into a trigger list for a retail bank or fintech:
- Outbound payments that cannot be recalled. Wires, push payments and instant transfers score highest on irrevocability. Our guide to push payment fraud prevention steps covers what happens when these move without a challenge.
- Adding or changing a payee. FFIEC’s customer remote access guidance lists restrictions on adding recipients, transaction limits, dual authorization and out-of-band verification among layered controls.
- Account-maintenance changes. FFIEC says institutions should control changes such as address or password changes made online or through customer service, and Red Flags guidelines point to verifying change-of-address requests for existing covered accounts.
- Credential and recovery changes. Password resets, new MFA enrollments and phone-number changes are the steps account-takeover crews pursue first, because they create persistence.
- Data export and access to customer information. FFIEC states in its retail payment systems booklet that single-factor authentication alone is inadequate for high-risk transactions involving access to customer information or movement of funds to other parties.
- Privileged or administrative actions. Back-office roles, API key creation and configuration changes deserve the same logic as customer payments.
OWASP adds a practical rule: require current credentials before sensitive account-information changes or transactions, and use context-aware reauthentication drawing on geolocation, device type and prior patterns.
Trigger category 2: the context has changed
Contextual triggers watch the session rather than the action. OWASP gives a new device or location, including a high-risk location, as examples of risk-based MFA triggers. FFIEC’s remote-access guidance similarly points to device authentication and location consistency as controls proportionate to remote-banking risk.
The signals that belong on most lists:
- New or unrecognized device. The first session from a browser or handset the institution has never bound to the customer.
- Location anomalies. Impossible travel, a country the customer never uses, or a network type that does not fit the profile. NIST notes that unexpected geolocation or an IP block associated with cloud services may prompt additional risk-based controls.
- Behavioral drift. Typing cadence, navigation sequence or session timing that departs from history. FFIEC identifies fraud monitoring based on customer history and behavior as a layered control.
- Velocity. Funds moving in and out quickly, many payees added in one sitting, or repeated small tests before a large transfer. FFIEC’s BSA/AML examination guidance flags anomalous account behavior and fund velocity, IP-address reports and linked accounts as indicators.
- Channel and origin. Non-face-to-face account openings and unusual remote deposit capture activity appear on the same FFIEC list.
- Session age. FFIEC also names application time-outs with mandatory reauthentication, which is a trigger based purely on elapsed time.
The limit NIST puts on signals
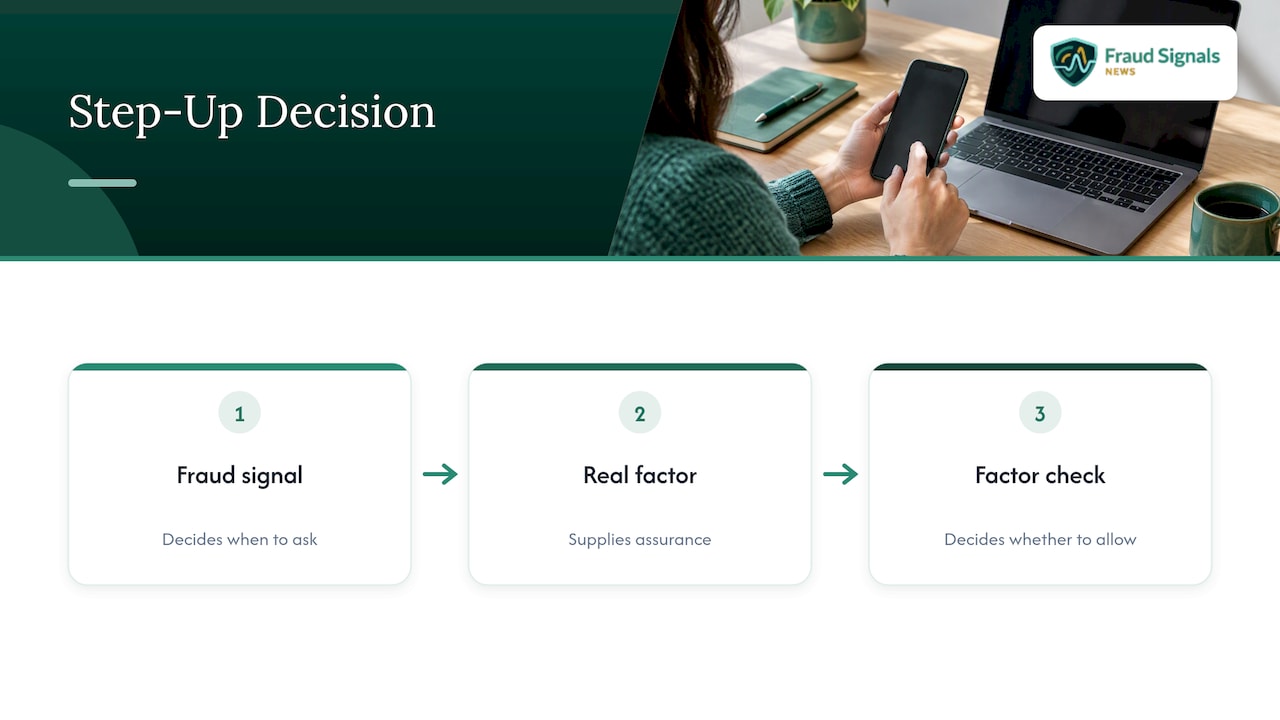
This is the point that most trigger designs get wrong. NIST states that fraud indicators do not change the authentication assurance level and cannot substitute for an authentication factor. A suspicious signal can tell you more assurance is appropriate. It cannot supply that assurance. If a risk engine says “this looks like the customer,” that is not a reason to skip the challenge on a high-value wire.
The practical consequence: use signals to decide when to ask, and use real factors to decide whether to allow.
Combining signals into thresholds
A single signal rarely deserves a hard challenge. A new device on a balance check is routine; a new device plus a new payee plus a first-ever international wire is a different story. The Federal Reserve guidance suggests the workflow: inventory systems, services, customers and transactions; assess the high-risk transaction factors; periodically evaluate authentication controls; and address residual risk according to a documented risk appetite and tolerance.
A workable threshold structure looks like this:
| Tier | Typical situation | Response |
|---|---|---|
| Low | Known device, usual location, read-only or low-value activity | No additional challenge |
| Elevated | One contextual anomaly, or a moderately sensitive action | Single step-up with a phishing-resistant method where available |
| High | Irrevocable or high-value action, or two or more anomalies together | Step-up plus out-of-band confirmation, holds or limits |
| Critical | Failed challenges, recovery-flow abuse, signs of compromise | Deny or hold, alert, route to the recovery and incident process |
Two cautions for tuning. First, document why each trigger exists, because the guidance expects thresholds to follow a stated risk appetite rather than habit. Second, measure the effect. NIST requires verifiers and credential service providers that use fraud indicators to assess their efficacy, mitigate negative effects on user populations and include them in privacy-risk assessments. A trigger that fires constantly on legitimate travelers, or on users of privacy tools, is a defect to fix, not a safe default.
For teams that want to see how static, rules-only stacks drift out of date, why outdated fraud prevention fails in financial services examines the pattern.
Choosing the challenge once a trigger fires
The trigger is only half the control. A weak challenge behind a good trigger still loses. NIST’s guidance, summarized for practitioners, points toward phishing-resistant FIDO2/WebAuthn passkeys or security keys and PKI-based authenticators, with approved authenticator-app or other possession-plus-knowledge or biometric combinations where suitable. SMS, voice and email codes sit lower, as fallbacks.
CISA, NSA, FBI and MS-ISAC reach the same place in their phishing guidance: FIDO- or PKI-based MFA is phishing-resistant, and where push MFA must remain, number matching reduces MFA-fatigue attacks. The Cyber Safety Review Board went further in its review of the LAPSUS$ attacks, recommending a move away from voice- and SMS-based MFA toward passwordless, FIDO2-compliant, phishing-resistant MFA and calling for stronger controls against SIM swapping.
A ranked set of challenge options for step-up:
- Passkey or hardware security key bound to the device, ideal for payments and credential changes.
- Authenticator app with number matching when push cannot yet be retired.
- Biometric with liveness, combined with another factor. FFIEC cautions in its biometrics booklet that a biometric identifier alone is one factor and may need combination with other technologies for high-risk transactions.
- Out-of-band confirmation of the specific transaction, with the payee and amount shown.
- SMS, voice or email codes only as a fallback, and ideally never for the highest tiers.
On biometrics, the details of capture integrity matter as much as the match. Our explainers on face liveness detection and liveness detection spoofing cover where these checks hold and where they break.
Support channels need triggers too
Fraudsters who cannot defeat the app go around it. FFIEC’s IT support guidance says support channels should use different authentication levels based on contact method, requested action, platform, system or data, with supplemental and out-of-band authentication for account-maintenance changes and high-risk transactions.
In practice, a caller asking to change a phone number or reset credentials should meet the same step-up the web customer would, not a few knowledge questions. That includes the common pattern in which a caller is verified by voice alone; see why voice biometrics alone fail in the contact center and layered call center authentication for how layered designs cut handle time without lowering assurance.
The same principle underlies access control security services: the identity check at the door and the extra check before a restricted area are separate decisions, and the second one is the step-up.
Handling a failed challenge
A failed step-up is itself a high-quality fraud signal, and the response should reflect that. NIST’s guidance, as summarized for implementers, supports a consistent playbook:
- Do not complete the action. Deny it or hold it for review. Never let the transaction proceed while the challenge is retried in the background.
- Rate-limit and log attempts. Repeated failures across a session, device or account should escalate the tier, not reset it.
- Alert and start recovery procedures when the pattern suggests compromise, and keep a defined incident-response path.
- Avoid revealing which factor or account detail failed. Specific error messages hand attackers a map.
Pair this with downstream controls such as transaction limits and dual authorization from FFIEC’s layered list, so that one successful challenge does not unlock unlimited movement.
Keeping triggers current against spoofing and deepfakes
Triggers written two years ago assume attacks that no longer dominate. NIST-aligned practice calls for updating signals and controls as methods change, including phishing, credential abuse, SIM swapping, push fatigue, spoofing and synthetic or deepfake-assisted impersonation. Do not treat a facial, voice or other biometric match as conclusive on its own: combine it with phishing-resistant possession, device, transaction, liveness and behavioral controls, keep assessing false positives and population impact, and maintain recovery paths for suspected compromise.
Two implications for trigger design. Recovery flows and new-device enrollment deserve the highest tier, because a convincing synthetic identity can pass a lightweight check at the moment of enrollment. And capture integrity, meaning whether the camera feed is genuine rather than injected, needs to be a signal in its own right. Our pieces on stopping deepfake ID fraud through capture integrity and replay and injection defenses go deeper. For the identity-proofing side that feeds enrollment, see NIST SP 800-63A identity proofing steps.
Perspective
Most step-up programs we see fail in one of two ways. Either they challenge too much, so customers learn to approve anything, or they rely on a risk score as if it were a credential. Both are the same mistake: treating the trigger as the control.
Our view is that the trigger decides when, and the factor decides whether. A score that looks reassuring should never excuse a weak challenge on an irrevocable payment, and a strong challenge is wasted if the recovery flow lets an attacker enroll a new device with a selfie and a guess.
That is why we keep returning to layered identity verification: biometrics with liveness, capture integrity, device binding and phishing-resistant factors working together, and tested against the attacks fraud teams actually see. Institutions that still lean on knowledge questions and SMS codes are running a commoditized defense that fraud rings have already defeated at scale.
Carlos Ochoa
Where to go next
If you are mapping triggers to a biometric layer, start with why biometrics reduce bank fraud and why biometrics satisfy compliance requirements. They cover the evidence for strong biometric assurance and how it lines up with regulatory expectations. For a broader view of the schemes your triggers must catch, our retail banking fraud schemes guide and ways to reduce identity fraud exposure are the practical companions.
Fraud Signals News tracks biometric identification, liveness detection, eKYC and deepfake ID developments for fraud, risk and compliance leaders in banking, fintech, healthcare and travel. Our analysis is written to help you decide which controls to modernize first.
Browse the latest coverage on the Fraud Signals News homepage, or start with our guide on selfie identity verification to see how the capture step shapes every downstream trigger.
FAQ
What is the most common trigger for step-up authentication?
The most defensible trigger is the sensitivity of the action, such as adding a payee, sending an irrevocable payment or changing credentials. Contextual signals like a new device or unusual location are the usual second layer. Federal Reserve guidance points to amount, volume, information sensitivity, irrevocability and fraud impact as the factors that mark a high-risk transaction.
Can a risk score replace the step-up challenge?
No. NIST states that fraud indicators do not change the assurance level and cannot substitute for an authentication factor. A risk score tells you when to ask for more proof. The proof itself must still come from a real factor such as a passkey, key or app-based authenticator.
Is SMS acceptable as a step-up method?
It is better treated as a fallback. NIST-aligned guidance ranks SMS, voice and email codes below phishing-resistant options, and the Cyber Safety Review Board recommended moving away from voice- and SMS-based MFA. If you must keep it, avoid it for the highest-risk actions and strengthen SIM-swap controls.
What should happen when a step-up challenge fails?
The action should be denied or held, attempts rate-limited and logged, and the account routed to protection and recovery procedures if compromise is suspected. Error messages should not reveal which factor or detail was wrong, since that helps an attacker refine the next attempt.
How often should step-up triggers be reviewed?
Periodically, and whenever attack patterns shift. Federal Reserve guidance calls for periodic evaluation of authentication controls against documented risk appetite, and NIST expects organizations using fraud indicators to assess their efficacy and their effect on user populations.
Sources
- NIST SP 800-63B-4, Digital Identity Guidelines: Authentication and Authenticator Management
- Federal Reserve, Authentication and Access to Financial Institution Services and Systems
- FFIEC IT Handbook, Customer Remote Access to Financial Services
- FFIEC IT Handbook, IT Support
- FFIEC IT Handbook, Retail Payment Systems information security
- FFIEC IT Handbook, Biometrics for Payment Initiation and Authentication
- FFIEC BSA/AML Manual, Risks Associated with Money Laundering and Terrorist Financing
- FTC, Identity Theft Red Flags and Address Discrepancies final rule
- OWASP Multifactor Authentication Cheat Sheet
- OWASP Authentication Cheat Sheet
- CISA, Phishing Guidance: Stopping the Attack Cycle at Phase One
- Cyber Safety Review Board, Review of the Attacks Associated with LAPSUS$
Recommended
Proof of Life Video: How Liveness Checks Work and Where They Fail
ISO 30107 Liveness: What Compliance Really Proves