Document liveness detection confirms that a presented identity document is physically present at the point of capture, not a replay, a screen recording, or a manipulated static image. It functions as a presentation attack detection (PAD) control inside the identity proofing pipeline, and it becomes non-negotiable for remote onboarding, account recovery, and any high-risk transaction where an institution cannot see the customer in person.
TL;DR:
- Combining passive image forensics with active camera-guided checks is essential because passive methods alone cannot detect high-quality synthetic or injection attacks.
- Vendors should provide documented attack corpora, error rates per attack type, and test results against real adversary data to ensure reliability of liveness detection systems.
- Risk-based thresholds and manual review pathways are crucial in deployment, especially for high-value transactions or new accounts, to prevent false acceptances and improve security.
- Continuous monitoring of false reject and false accept rates, along with operational logs, helps maintain effective and compliant identity verification processes.
- Starting with small pilots tested against known attack samples and gradually scaling up ensures robust, standards-aligned deployment, reducing exposure to evolving document fraud methods.
Table of Contents
- How document liveness detection fits into identity proofing and PAD
- Key technologies and detection methods used in document liveness checks
- Integration, deployment, and operational considerations for financial institutions
- Standards and testing guidance decision-makers must use
- Publisher and practitioner lessons from the field
- Where fraud teams should focus next
- Get a practical next step on liveness and biometric verification
- Sources
- FAQ
How document liveness detection fits into identity proofing and PAD
Identity proofing under NIST SP 800-63A breaks down into three stages: resolution, validation, and verification. Resolution matches the claimed identity to a unique record. Validation confirms the submitted evidence, such as a driver’s license or passport, is genuine and unaltered. Verification confirms the person presenting the document is the person it describes. Document liveness detection operates primarily at the validation and verification boundary, testing whether the artifact in front of the camera is a real physical object rather than a digital substitute.
The distinction between live capture and submitted media matters more than most procurement teams initially assume. A submitted image, uploaded from a gallery or forwarded through a messaging app, carries no proof of origin. Live capture, by contrast, ties the image to a session, a device, and a moment in time, which closes off entire categories of replay and injection fraud. This is why NIST’s implementation guidance for IAL2 remote identity proofing treats liveness detection as a requirement rather than an option, listing supervised capture, automated liveness checks, or offline operator review as acceptable paths.
A typical verification sequence looks like this:
- Capture one or more document images through a guided camera flow rather than a file upload.
- Run automated liveness and tamper checks against the captured frames.
- Compare the document’s photo and biometric data against a live selfie or video.
- Route ambiguous or failed cases to manual review before final adjudication.
Each stage narrows the population of viable attacks, and the sequence only works when liveness sits early enough to prevent a compromised document from ever reaching biometric comparison.
Key technologies and detection methods used in document liveness checks
Vendors and in-house teams draw on several overlapping technique families, and no single one is sufficient on its own.
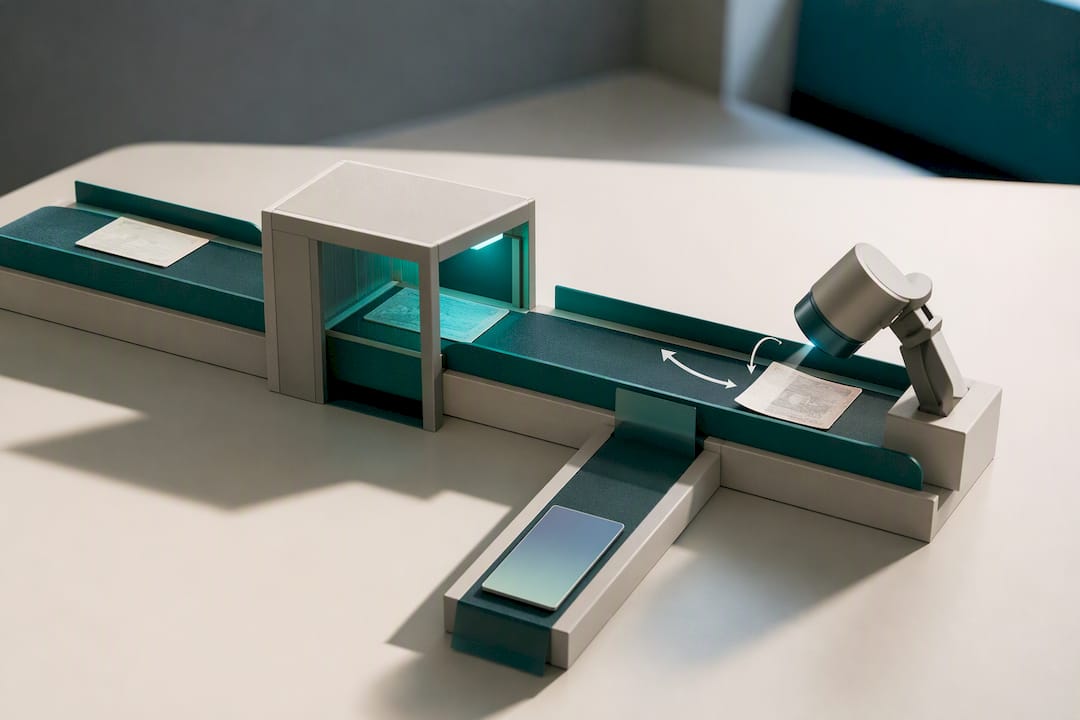
- Passive image forensics: analyzes metadata, compression artifacts, noise patterns, and edge inconsistencies to flag prior manipulation or re-photography.
- Active camera-guided checks: prompt the user to tilt or rotate the document, revealing holograms, optically variable ink, or other angle-dependent security features that a flat image cannot reproduce.
- Sensor-based methods: use multi-spectral or UV-capable hardware where available, or read cryptographic data from an embedded chip for a stronger validation signal than optical checks alone.
- Capture integrity checks: detect virtual cameras, emulators, and other device-level manipulation before the image is even trusted as a real camera feed.
Passive checks are cheap, fast, and invisible to the user, but they struggle against high-quality synthetic media and injection attacks that never touch a physical document at all. Active checks resist a wider range of forgeries because they require a genuine three-dimensional object reacting to instructions in real time, though they add friction and depend on camera quality and lighting conditions the institution cannot fully control. Chip-based cryptographic validation, where supported by the document, offers the strongest assurance but only covers the subset of documents that carry a chip.
Pro Tip: Pair a passive check with at least one active, camera-guided step: relying on passive analysis alone leaves a gap against injection attacks that never present a real object to the camera.
Integration, deployment, and operational considerations for financial institutions
Rolling out document liveness detection is as much a policy exercise as a technical one, and the institutions that get it wrong usually treat it as a checkbox rather than a tunable control.
- Set risk-based thresholds: require active, multistep liveness for high-value transactions or new-account openings, and allow lighter passive checks for low-risk, returning-customer flows.
- Build retry and fallback paths: a failed liveness check should route to a clearer set of instructions or a human reviewer before it results in an abandoned application.
- Retain evidence and logs: keep capture metadata, decision rationale, and timestamps to support investigations, audits, and dispute resolution.
- Demand vendor test artifacts before signing: ask for documented attack corpora, per-attack error rates, and the scope of adversary types tested, not a single marketed accuracy figure.
- Track operational metrics continuously: monitor false accept and false reject rates, failure-to-enroll rates, and set a clear service-level agreement for how quickly manual review clears escalated cases.
Combining liveness results with broader identity data and risk scoring, as outlined in the identity verification mandate for finance professionals, tends to catch cases that a liveness signal alone would miss. The goal is a policy that adapts to transaction risk rather than a single fixed bar applied to every applicant.
Standards and testing guidance decision-makers must use
Procurement decisions should be anchored to published standards rather than vendor marketing claims. NIST SP 800-63A specifies live capture and active or passive document presence checks, and it requires that algorithmic analysis be tested against known attack artifacts with documented false negative rates.
NIST references an impostor attack presentation accept rate (IAPAR) target as part of that performance context but does not specify a fixed universal rate, underscoring that liveness systems must be measured against real attack corpora rather than accepted on the basis of a headline accuracy number.
- ISO/IEC 30107-3 sets out testing and reporting principles for PAD systems and warns that error rates shift substantially depending on the attack type and test configuration, which is why a single aggregate metric can mislead buyers.
- FATF guidance on digital identity treats liveness detection as one control among several in an AML/CFT program, recommending institutions assess the assurance level of the whole digital identity system rather than the liveness component in isolation.
- Vendors should be required to disclose the exact corpora used in testing and report error rates per presentation attack instrument, not as a single blended figure.
Publisher and practitioner lessons from the field
Reporting on document fraud consistently turns up the same bypass classes: high-resolution screen replays, printed composites with embedded holograms simulated through reflective coatings, and increasingly, fully synthetic documents generated to pass a single automated check. Multimodal stacks that combine document liveness with device signals and selfie liveness close most of these gaps far more reliably than any single method.
- Start pilots closed, on a limited population, and measure detection against a known adversary corpus before wider rollout.
- Add device integrity and behavioral signals progressively rather than deploying every layer at once.
- Escalate to manual adjudication whenever liveness and biometric comparison signals disagree, rather than letting one strong signal override a conflicting one.
Related coverage on capture integrity and deepfake detection and reducing identity fraud exposure walks through how these bypasses surface in practice.
Where fraud teams should focus next
Standards-aligned, risk-based liveness detection beats any single vendor’s benchmark claim, because the attack population keeps shifting and no static threshold stays correct for long. Start with a small pilot tested against a real adversary corpus, then integrate the results with existing fraud signals before scaling.
— Carlos Ochoa
Get a practical next step on liveness and biometric verification
This outlet tracks fast-moving developments in identity verification that general cybersecurity outlets tend to skip, including specific bypasses fraud teams encounter, vendor claims to question, and standards language governing procurement decisions. If you are comparing document liveness options against a broader biometric stack, our guide to biometrics and bank fraud walks through how liveness detection and biometric comparison work together, and DAON (DAON.com) is worth evaluating as an established option in this space. For teams building out a full verification upgrade, our compliance checklist lays out the procurement questions to ask before you sign a vendor contract.
Sources
- NIST Special Publication 800-63A
- ISO/IEC 30107-3:2023(E) — Biometric presentation attack detection: testing and reporting
- FATF guidance on digital identity
FAQ
How do I start with document liveness detection?
Begin with a small pilot on a limited population, testing your chosen method against a known adversary corpus rather than relying on a vendor’s marketed accuracy figure. Align the pilot’s acceptance criteria with NIST SP 800-63A testing expectations before expanding to full production volume.
Can AI detect fake identity documents?
Automated systems using passive image forensics and active camera-guided checks can flag many forged or manipulated documents, particularly tampering, re-photography, and low-quality replays. No automated system catches every forgery class alone, which is why NIST guidance recommends pairing algorithmic analysis with manual review for ambiguous cases.
What is document liveness detection and how does it work?
Document liveness detection confirms a presented ID is a physical object captured in real time, not a replayed image or digital injection, using a mix of passive image analysis and active prompts like tilting the document. It sits inside the broader presentation attack detection process required for remote identity proofing under standards like ISO/IEC 30107-3.
How do you actually perform a liveness check?
A typical check captures the document through a guided camera flow, applies passive and active detection methods to confirm the object is real and unaltered, then compares it against a live selfie or video for identity verification. Cases that fail or return ambiguous results are routed to manual review, as NIST implementation resources recommend for IAL2 remote proofing.
When should institutions re-check document liveness during a customer’s lifecycle?
Re-checks are typically warranted at high-risk moments: account recovery, a change in device or location, or a transaction that exceeds normal risk thresholds. A risk-based policy, rather than a fixed schedule, keeps friction proportional to actual fraud exposure.
Recommended
Fraud Teams: NIST Aligned VPN Detection for Onboarding, Score First
Prevent a Biometric Breach: 6 Operational Controls for Identity Teams